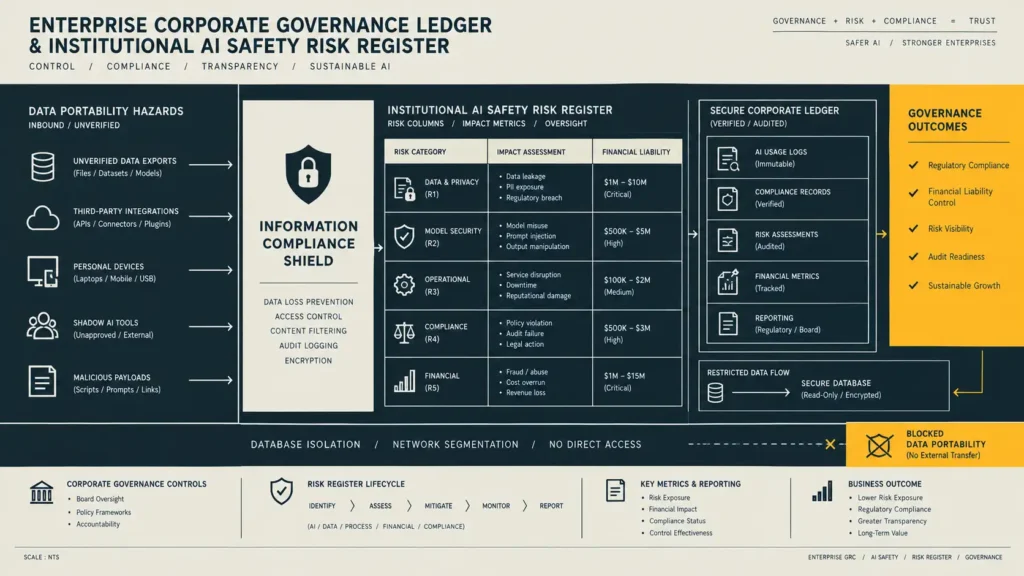
AI Safety Risk Register: 4 Masterful Frameworks to Stop Compliance Drift
Establish a robust AI safety risk register to clear enterprise procurement loops. Quantify model liabilities, track shadow tools, and secure compliance parameters.
Establish a robust AI safety risk register to clear enterprise procurement loops. Quantify model liabilities, track shadow tools, and secure compliance parameters.
Map out standard ISO 27001 AI controls across modern model infrastructure perimeters. Translate Annex A clauses into actionable data workflows to pass audit sweeps.
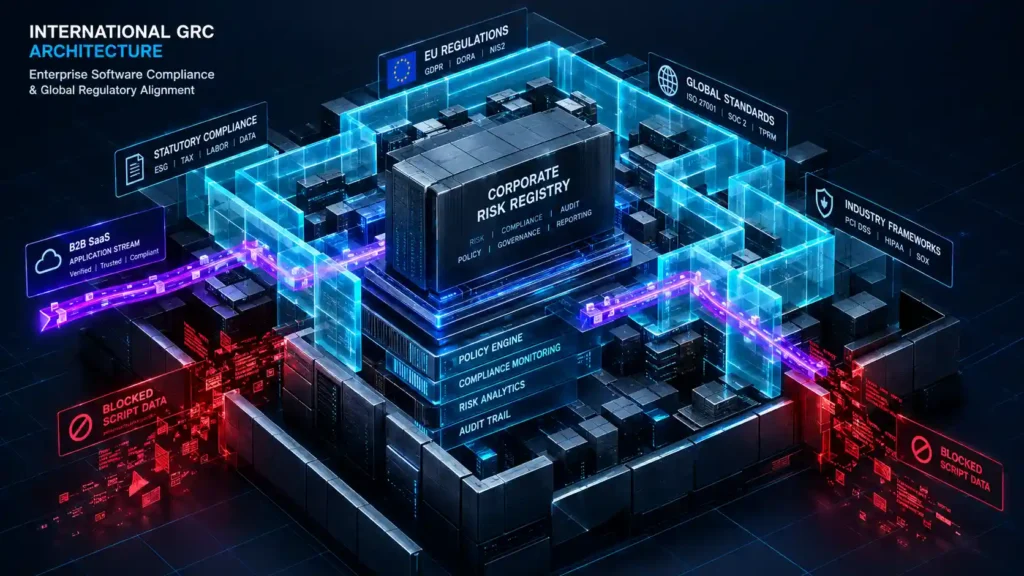
Achieve EU AI Act compliance for your B2B SaaS. Apply a 4-step growth-stage GRC roadmap to audit risk tiers, configure logs, and secure European market access.
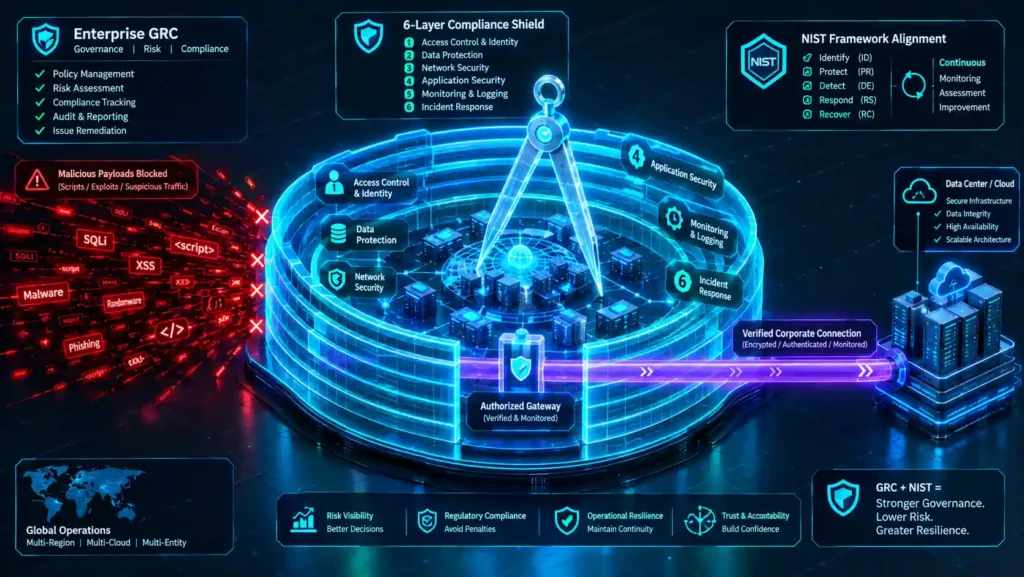
Learn how to achieve a nist framework alignment for small teams. Apply a 6-step GRC roadmap to configure access policies and secure system perimeters.
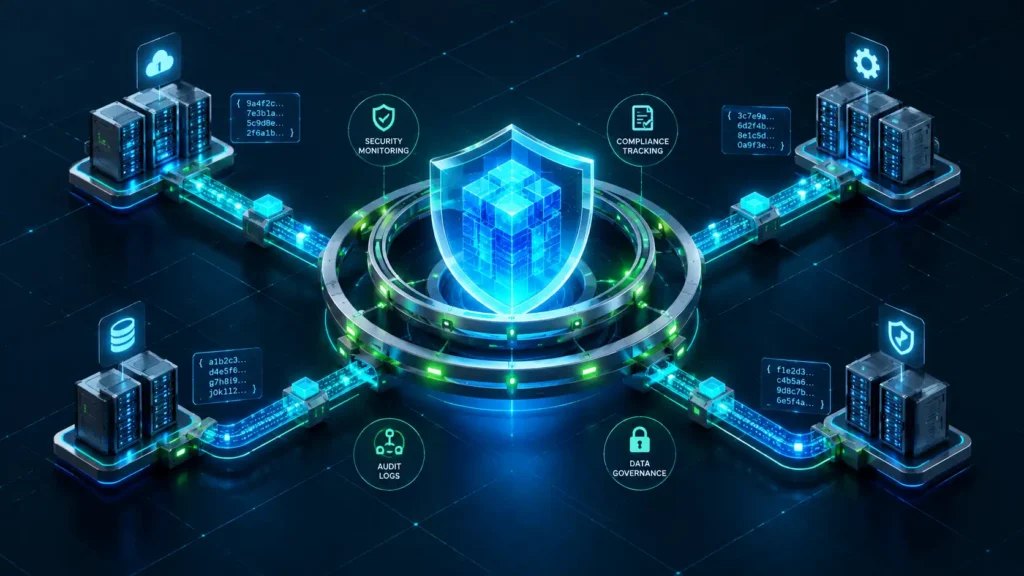
Learn how to scale b2b software startups grc frameworks seamlessly. Apply a 9-step architecture to automate controls, clear audits, and lock down compliance.
Master investor-grade risk modeling. Learn how high-growth scaleups prepare modular risk registers to protect valuations and eliminate funding pitfalls.
Learn conducting a HIPAA assessment via 4 rigid control measures. Implement strict data encryption, access controls, and business associate agreements.
Learn implementing NIST frameworks using 6 proven playbooks. Map out NIST CSF core functions, identify threat surfaces, and secure small business data assets.
Secure corporate trust. Learn passing a SOC 2 audit via 5 rigid compliance controls to streamline evidence collection and eliminate security risks.