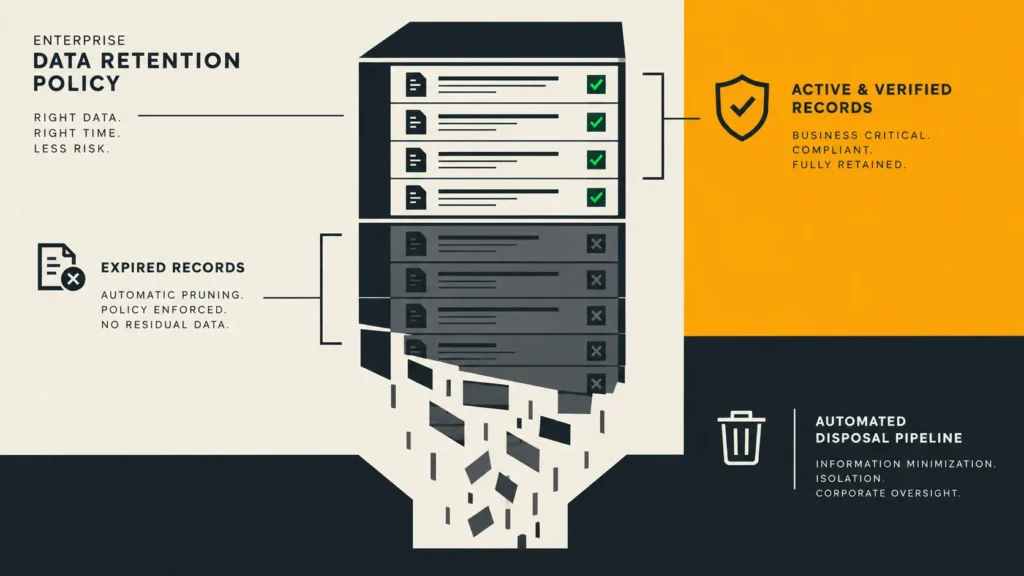
Data Retention Policy: 4 Practical Rules to Stop Compliance Drift
Formulate a strict data retention policy to systematically purge stale corporate records. Hardcode database pruning rules to satisfy global GDPR and HIPAA compliance mandates.
Formulate a strict data retention policy to systematically purge stale corporate records. Hardcode database pruning rules to satisfy global GDPR and HIPAA compliance mandates.
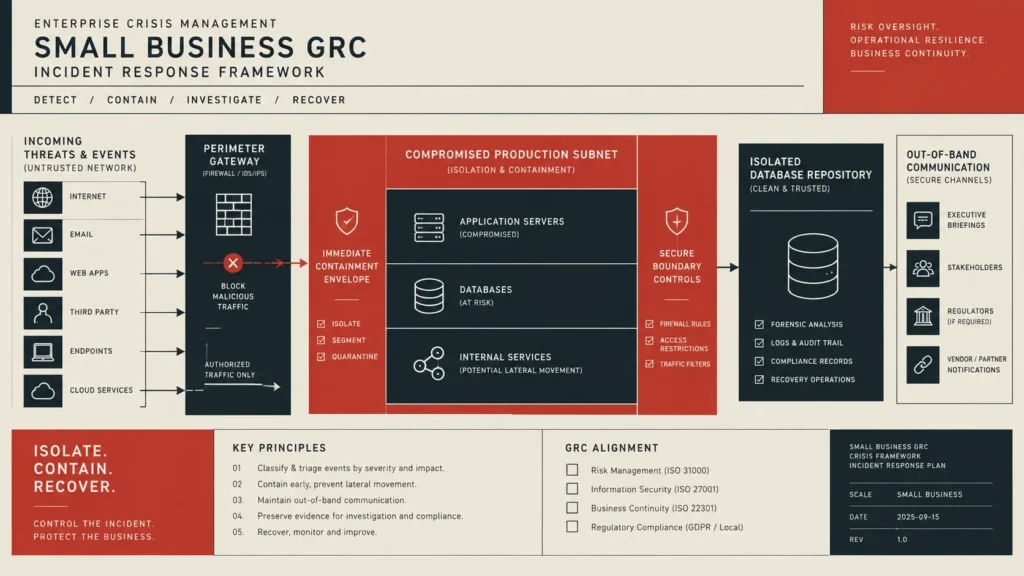
Learn how to write incident response plan files for lean, bootstrapped operations. Establish clear triage metrics, communication trees, and containment maps.
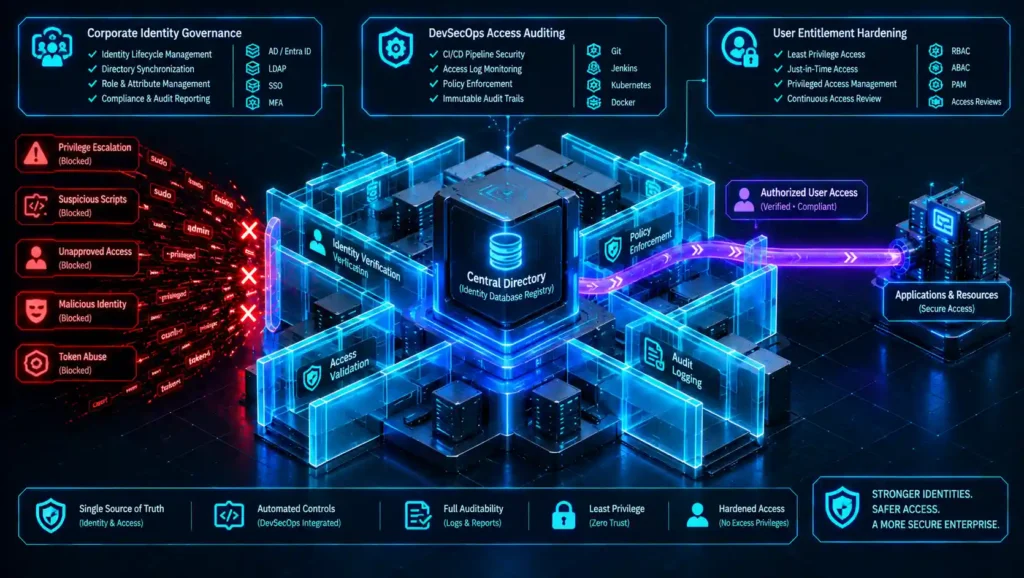
Deploy an automated access review framework for small teams on a limited budget. Apply a 4-step identity audit workflow to satisfy SOC 2 and ISO requirements cleanly.
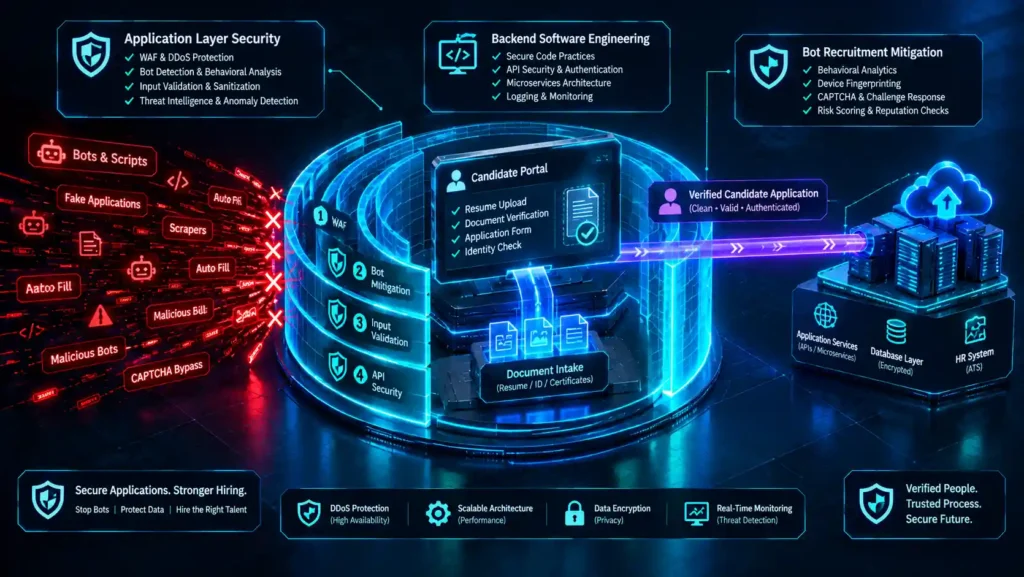
Learn how to block credential stuffing and malicious bot applicants inside corporate recruitment panels. Apply a 4-step framework to secure gateway perimeters.
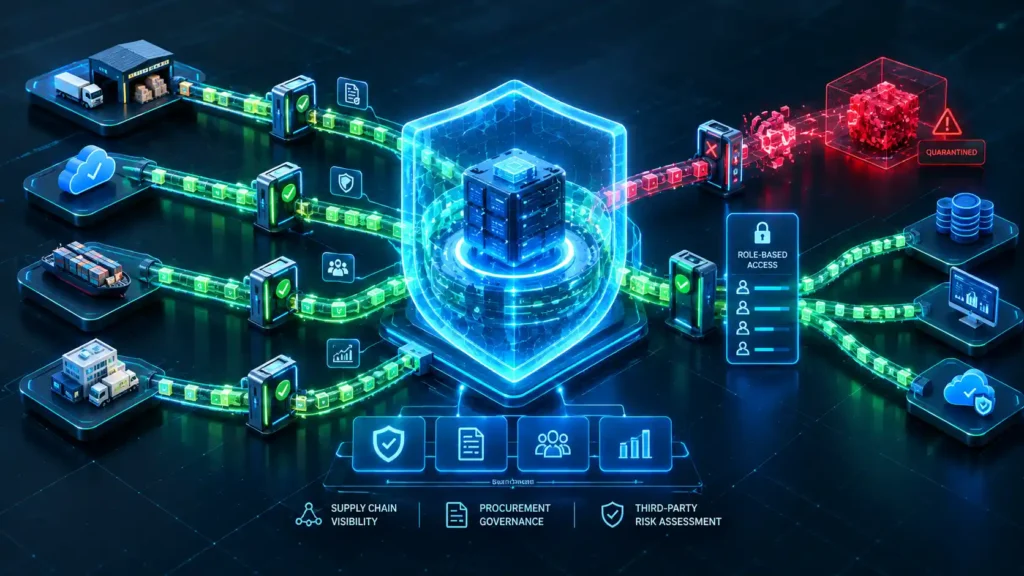
Learn how to manage supply chain threats. Apply a 5-step framework for vetting third party saas vendors using robust risk assessment standards to secure data.
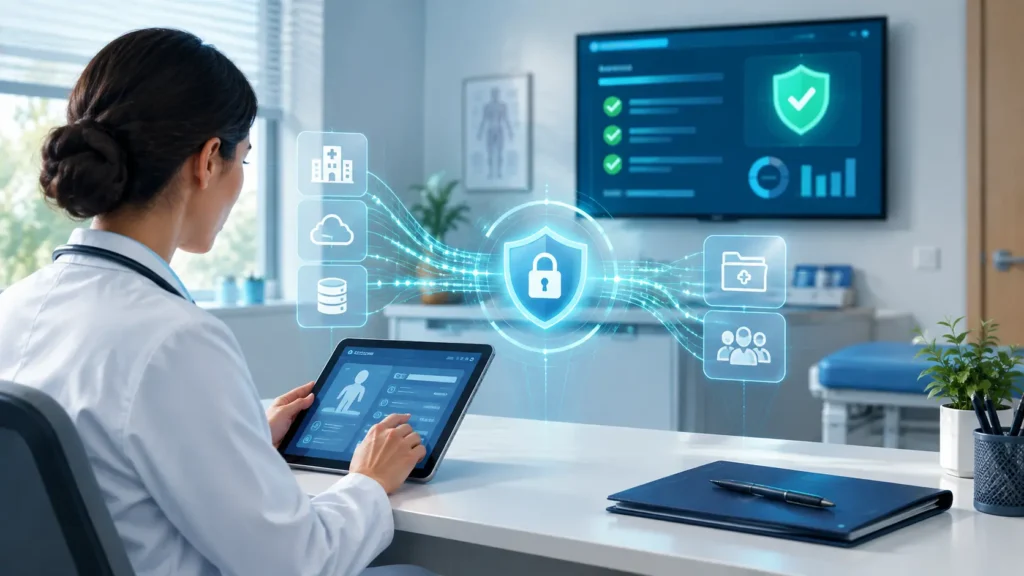
Master small business HIPAA compliance. Implement 4 core data governance policies, manage BAA lifecycle loops, secure ePHI, and avoid devastating federal fines.
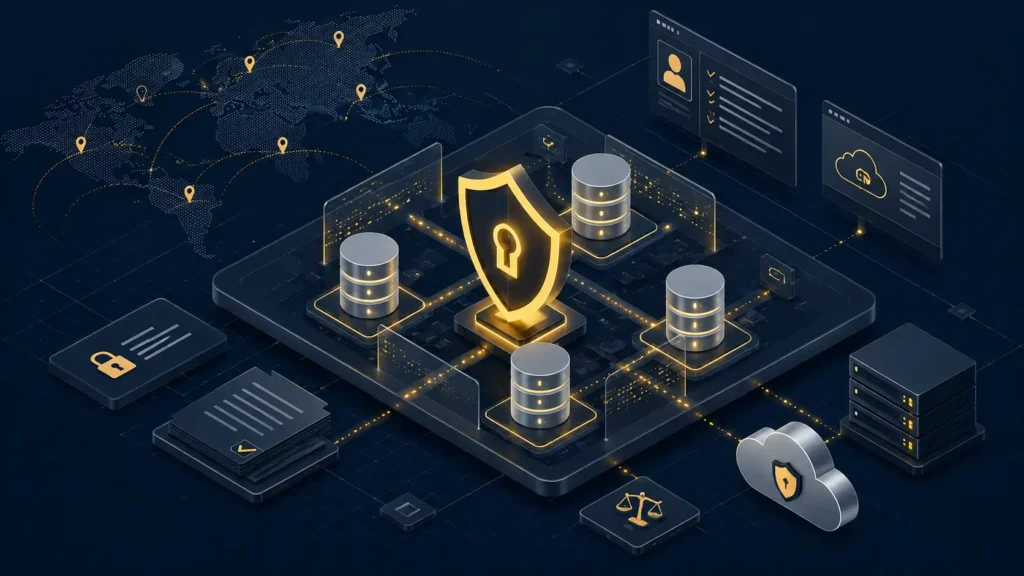
Master GDPR for startups. Implement 5 rigid data privacy controls, secure user consent loops, isolate data storage pools, and prevent regulatory fines.
Learn conducting an ISO internal audit via 4 clean checklists. Discover how to identify non-compliance gaps and pass your formal certification review.
Learn building an ISMS framework in 5 strategic steps. Align with ISO 27001 standards, implement administrative risk controls, and pass external audits.
Learn understanding ISO 27001 foundations using 6 practical rules. Build an Information Security Management System (ISMS) scaled for small business data.